
News

Share
Published 17:15 4 Nov 2026 GMT
Updated 17:15 4 Nov 2026 GMT
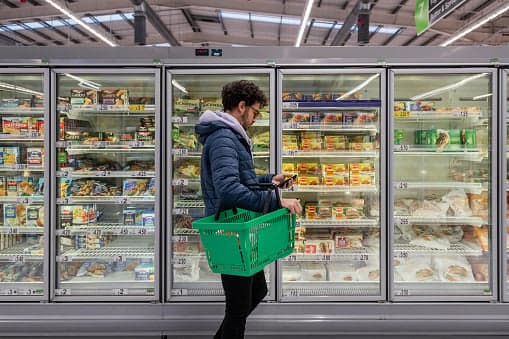
Weak security may have been the key to a series of freezer failures affecting supermarkets across Europe, with cyber-security researchers suggesting the systems were targeted using relatively simple techniques.
Ryan Dewhurst, from Spanish firm Previdian, said attackers appeared to collect the public IP addresses of individual freezers before creating a list of systems to target. They then struck overnight, when temperature changes could have the greatest impact.
The software involved was not particularly difficult to exploit, Dewhurst said.
The freezers relied on security measures that could be bypassed using attack methods already known to researchers and available online.
The timing of the incidents has raised suspicions that the disruption was deliberately coordinated.
Three cyber-security firms have been monitoring decoy freezer systems, known as honeypots, which are designed to attract attackers and record their activity.
Evidence gathered from the traps suggests the latest failures were part of a planned second wave, following a suspected attack days earlier.
"The fact that all these fridge freezers were hit simultaneously suggests planning and coordination," Dewhurst said.
While the precise source remains unknown, researchers say the evidence points towards an organised operation.
Two Russian hacktivist groups, Noname057(16) and Z-Pentest Alliance, have claimed they were responsible.
The BBC reported that the groups posted a message on Telegram before deleting it shortly afterwards, declaring they had "once again demonstrated a high level of skill and precision".
The claim has not been independently confirmed. Investigators have not excluded Russian involvement, but say other possibilities include an Iranian hacktivist group, a nation-state operation or an individual acting alone as a prankster.
A separate investigation by Strathclyde-based cyber-security firm Lupovis has used honeypots deployed worldwide to track the attackers' behaviour and determine what they might do next.
Researchers have not yet identified those behind the freezer disruptions, and say a definitive answer may not emerge for some time.
Explore more on these topics:
News
News
News
News
Nearly 1,500kg NASA spaceship could come crashing back to Earth within hours
Retired NASA observatory set for fiery return A retired Nasa observatory is making its final journey back to Earth, with a small chance that fragments surviving reentry could injure someone. The Neil Gehrels Swift Observatory weighs close to 1,500kg, and estimates put the risk at around one in 2,500. Most of the spacecraft is expected […]
News
5h
‘Democrats did a good job’ – Trump accepts election defeat for the first time in his life
The Democrats won so comprehensively in the midterms that even Trump can’t try and deny these results. There have been some surprising results in the US midterm elections after the Democrats regained control of the House of Representatives and the Senate. But perhaps the most shocking turn of events is this: Donald Trump is actually […]
News
7h
‘Bomb alert’ forces emergency landing of flight from London
News